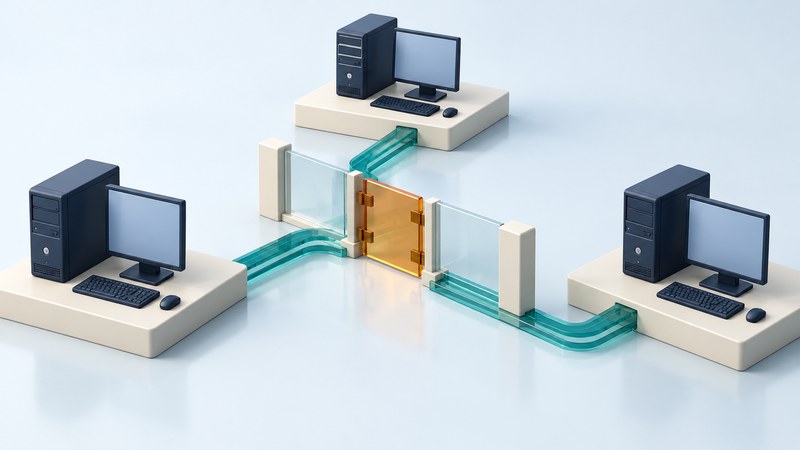
Sasser is a useful counterexample to the idea that avoiding suspicious attachments is enough to stop every worm. Its 2004 spread depended on a vulnerable Windows service reachable over a network. Understanding that route makes patch verification and network boundaries easier to reason about.
This is a historical case study, not a procedure for repairing a current computer. For a present-day problem, start with the malware response guide.
Read the outbreak beside the patch date
Microsoft published MS04-011 on April 13, 2004. The bulletin addressed several vulnerabilities, including the LSASS issue relevant to Sasser. A bulletin’s complete affected-product list is not the same thing as the set of systems a particular worm successfully infected.
By early May, Sasser was spreading. In its May 2, 2004 statement, Microsoft identified the targeted LSASS vulnerability and the already-released update. The sequence matters: availability of a fix preceded the outbreak, but availability did not establish that exposed machines had received it.
Microsoft’s Sasser family analysis describes network worms exploiting the Local Security Authority Subsystem Service vulnerability, with propagation among affected Windows 2000 and Windows XP systems. Historical restarts or service failures are part of the case record; a restart today is not a Sasser diagnosis.
Follow the exposure rather than the message
- A service is vulnerable. The relevant software flaw is present on the target.
- Another system can reach it. Network access supplies the opportunity to interact with that service.
- The worm exploits the service. The route does not depend on persuading that user to open an email attachment.
- The newly infected machine becomes another source. A local compromise can become a problem for other reachable systems.
This is a conceptual account of the historical route, not an exploit recipe. It separates two questions defenders can investigate: whether a machine has vulnerable code, and whether traffic can reach it. Reducing reachability and fixing the code address different parts of the chain.
It also explains why user education and technical maintenance are complementary. An employee can follow every email rule while an exposed service remains vulnerable. Conversely, installing a patch for one service does not make a deceptive attachment harmless.
Tabletop exercise: the returning laptop
A useful answer identifies records and owners: an asset list, a device-specific result and a process for exceptions. “We sent the update” describes an action; “we verified these devices and isolated these exceptions” describes a more complete result.
Carry forward the questions, not the old cure
- Which services are exposed, and who maintains each one?
- Which devices are missing from the update report?
- Can one compromised workstation reach systems it does not need?
- How are failed or delayed updates escalated?
- What evidence is required before an affected machine returns to normal use?
The internal-network containment guide develops the boundary questions; the Zotob case study focuses on patch coverage. Neither should be read as a reason to keep a period Windows system connected using a decades-old patch recipe. Supported software and an appropriate recovery plan remain separate decisions.
Keep historical filenames, risk ratings and affected versions attached to their dates. They help explain the outbreak, but they are not reliable standalone indicators for investigating a different computer today.