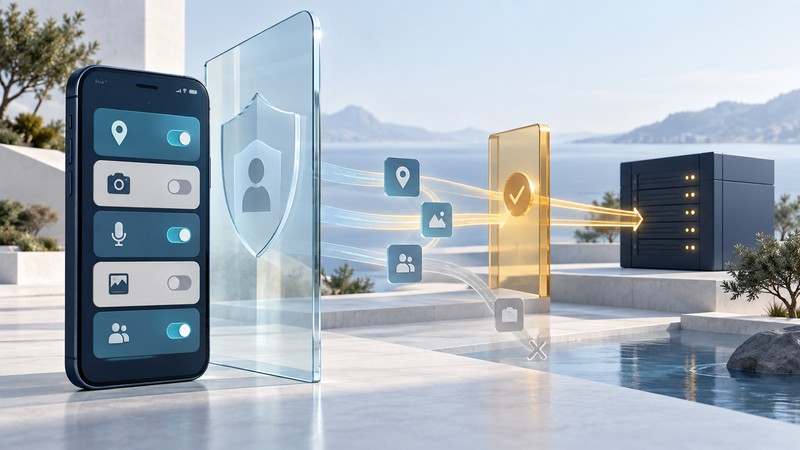
A useful mobile-app review connects each requested permission and data flow to the work the app must perform. Start with a specific task, then establish what information enters the app, where it goes and who can retrieve it. Record unknowns before approving wider use.
This guide is for a small organization choosing an app. It supports an adoption decision; specialist testing is needed to establish technical security properties. Use a test account and invented records, with authorization to review the app and its service.
Define the app and the data
Record the publisher, official distribution link, app version, operating system, business owner and intended task. Identify the service behind the app and any separate account administrator. A familiar app name alone leaves too much ambiguity for a repeatable review.
List the data involved: photographs, customer details, location, files, contacts and identifiers. Distinguish information a worker enters from information the app requests automatically. Ask the supplier which service providers receive it, where retention rules are documented and how deletion requests are handled.
On a narrow screen, scroll sideways. Keyboard: focus the table and use the arrow keys.
| Area | Question | Evidence |
|---|---|---|
| Purpose | Which work result requires this app? | One representative task and its required fields |
| Permissions | Which access is necessary, and when? | OS permission settings and observed prompts |
| Data handling | Where are records stored, shared and retained? | Dated supplier documentation and contract terms |
| Accounts | Who can add, remove and recover access? | Demonstrated admin and recovery procedures |
| Assessment | Which version and components were tested? | Report scope, date, findings and remediation status |
OWASP MASVS organizes mobile-app security into areas including storage, authentication, network communication and privacy. Use those areas to request relevant evidence. A statement that an app follows a standard needs an identified assessment scope and result.
Test access against the actual task
Install through the verified publisher route. Read each permission prompt and connect it to an action. A camera permission may support photographing a receipt; continuous location access needs its own purpose. Try the task with optional access declined and record what changes.
On Android, Google’s permission guidance describes per-app controls under Settings, Apps and Permissions. Available choices depend on the permission, device and Android version. Use the equivalent documented controls for the actual platform in your pilot.
OS permissions describe access to protected device functions. They do not provide a complete inventory of what the app transmits or how its backend uses submitted records. Review the supplier’s data handling alongside the phone’s settings.
Separate observed behavior from assurance
Complete a normal task, sign out, and check what remains visible in the app, notifications and exported files. Ask an authorized administrator to remove the test account’s access and verify the documented result. Perform these checks only with test data and accounts you control.
Ask for the date and version of any assessment, the tested mobile and backend components, important exclusions and evidence that significant findings were resolved. Have a qualified reviewer examine the report when the app handles sensitive information or broad account privileges. Keep confidential reports in the organization’s approved store.
Fictional review: a receipt app completes a test submission with camera access but also requests background location. The reviewer records that location is unnecessary for the defined task, disables it, repeats submission and asks the supplier to explain the request. Successful submission establishes task compatibility with that setting; it does not establish every aspect of the app’s security.
Make a decision with an owner
Choose approval for a defined use, a limited pilot, further assessment or rejection. Name unresolved questions, their owners and the evidence required to close them. Record the accepted app version, settings, data types and account arrangement.
Revisit the decision when permissions, supplier ownership, data recipients, authentication or supported platforms change. Download the editable app-review sheet to retain the task, observations, evidence and approval boundary together.
Use mobile-device security for enrollment, loss response and retirement, and mobility strategy to plan the wider rollout.