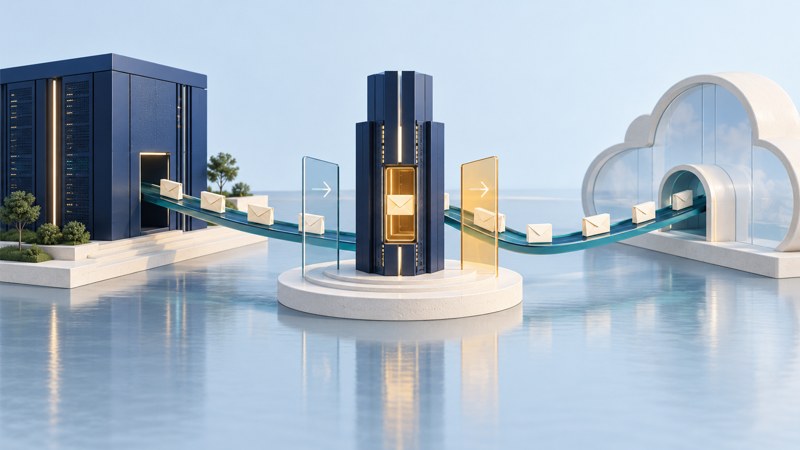
An Exchange Edge Transport server is a mail-processing role at the organization’s perimeter. It provides a defined place for internet mail relay and associated controls, while internal Exchange servers handle their own transport and mailbox responsibilities.
Microsoft’s 2004 Exchange Edge Services announcement described a proposed approach to protecting mail at the network boundary. Today’s deployment decisions should follow the documented Edge Transport role and the support requirements for the installed environment.
Place the role on the mail route
In Microsoft’s documented Edge design, inbound internet mail is processed by Edge and routed to an internal Mailbox server. Outbound internet mail reaches Edge after processing on the internal server. Edge can resolve destinations through DNS or forward mail to a smart host. Its agents and rules apply additional message controls. See Microsoft’s Edge Transport overview.
Start a review by drawing the actual routes, including any hosted filtering provider. Locate the public receiving service, internal relay, sending service and destination. Record where each route changes ownership. This makes it possible to locate a delivery failure without assuming that every message passed through the same system.
Illustrative route: external sender → the organization’s configured receiving service → Edge, if used on that route → internal Exchange transport → recipient mailbox. Reverse-direction mail and cloud mailboxes need their own route descriptions.
Understand the directory boundary
An Edge server operates outside the internal Active Directory forest. It keeps required configuration and recipient information in a local AD LDS instance. EdgeSync replicates the relevant information from the Exchange organization. This is a limited data flow for mail operation, not unrestricted directory membership.
Microsoft’s Edge Subscription documentation explains what is synchronized and when a subscription is needed. For a review, record which server is subscribed, the responsible site, the latest successful synchronization and the owner of failures. Use the documented process for the installed version; subscription changes can affect connector configuration.
Trace hybrid mail separately
In a hybrid design that uses Edge for hybrid transport, Edge relays mail between internal Exchange servers and Microsoft 365. Microsoft describes Edge as an optional role in that arrangement. Its hybrid Edge guidance warns that intermediate services which modify messages can affect how those messages are treated.
Draw both directions, identify the expected sending and receiving connectors, and establish which systems are permitted to modify a message. Document certificate ownership, renewal and expiry monitoring. The certificate and connector expectations must agree with the supported hybrid design.
Sender authentication, malware checks, routing and TLS answer different questions. A message can pass one check and fail another. Keep those findings separate when explaining an incident or a delivery problem.
Give each recurring check an owner
- Mail flow: queues, delivery failures, expected routes and meaningful test messages.
- Synchronization: current recipient/configuration data and the response to failed updates.
- Certificates and DNS: renewal responsibility and the impact of changes.
- Rules and exceptions: purpose, scope, expected behavior and review dates.
- Platform support: the exact Exchange build, operating system and supported combination.
As checked in October 2026, Microsoft’s supportability matrix identifies Subscription Edition as the supported Exchange Server line and records the October 14, 2025 end of support for Exchange 2016 and 2019. Older versions can remain mentioned in architecture documentation; that mention alone does not establish current support.
Fictional example: one direction fails
A hybrid organization can receive mail from the cloud but cannot send along the expected reverse route. The team records a test message reference and follows the sending-side queue and connector evidence. It checks the route’s certificate and connection requirements before changing unrelated filtering policies.
Once corrected, the team verifies both directions and documents the cause. The investigation produces a specific finding, rather than a blanket exception for the affected domain.
For filtering decisions and quarantine ownership, continue with the email security gateway guide.